











77.100.51.198.bl.spamcop.net
→ 127.0.0.2
→ 127.0.0.2
Listed SpamCop
The list has the address. The code says why, and the list's TXT note often links to its own page about it.
Check an IP, mail server or domain against 27 live blacklists and reputation lists. See why you're listed, who owns the address and how to delist.
IPv4 or IPv6. A domain or e-mail address checks its mail servers and its web address.
Sent to the blocklists below as DNS questions, through Google and Cloudflare DNS. Kept 10 minutes, then dropped.
An IP blacklist, or DNSBL (DNS-based blocklist), is a list of addresses that sent spam, attacked servers or shouldn't send mail directly, published as a DNS zone so any mail server can look an address up in milliseconds. Receiving servers ask one or more lists for every connection, then reject the message or add to its spam score when the address is listed.
The question is the address written backwards in front of the list's zone: to check 198.51.100.77 on SpamCop, a server asks for 77.100.51.198.bl.spamcop.net. No such name (NXDOMAIN) means not listed; an address in 127.0.0.0/8 means listed, and its last number says why. IPv6 addresses are asked as 32 reversed hex digits (RFC 5782).
The lists block nothing themselves: each receiving server's admin decides which lists to trust and what a listing costs a message. Every list must list 127.0.0.2 and never 127.0.0.1, its built-in test, which this checker asks with every check.
bl.spamcop.net77.100.51.198.bl.spamcop.net A ?Two possible answers
127.0.0.2SpamCop's code: reported as spam in the last 24 hours
NXDOMAINThe name doesn't exist: the address isn't on the list
Every list's test: 2.0.0.127.bl.spamcop.net must answer 127.0.0.2
Type the address in the box above, or use Your IP. Every list answers in one of six ways, and only two of them say something about the address: listed and not listed. A list that refuses or stays silent tells you nothing, so it never counts as clean.
The verdict names the major lists first. The chart under it shows every list as a cell as wide as its weight, so one SpamCop listing outweighs three small ones at a glance, and the score compares the listed weight with the weight that answered.
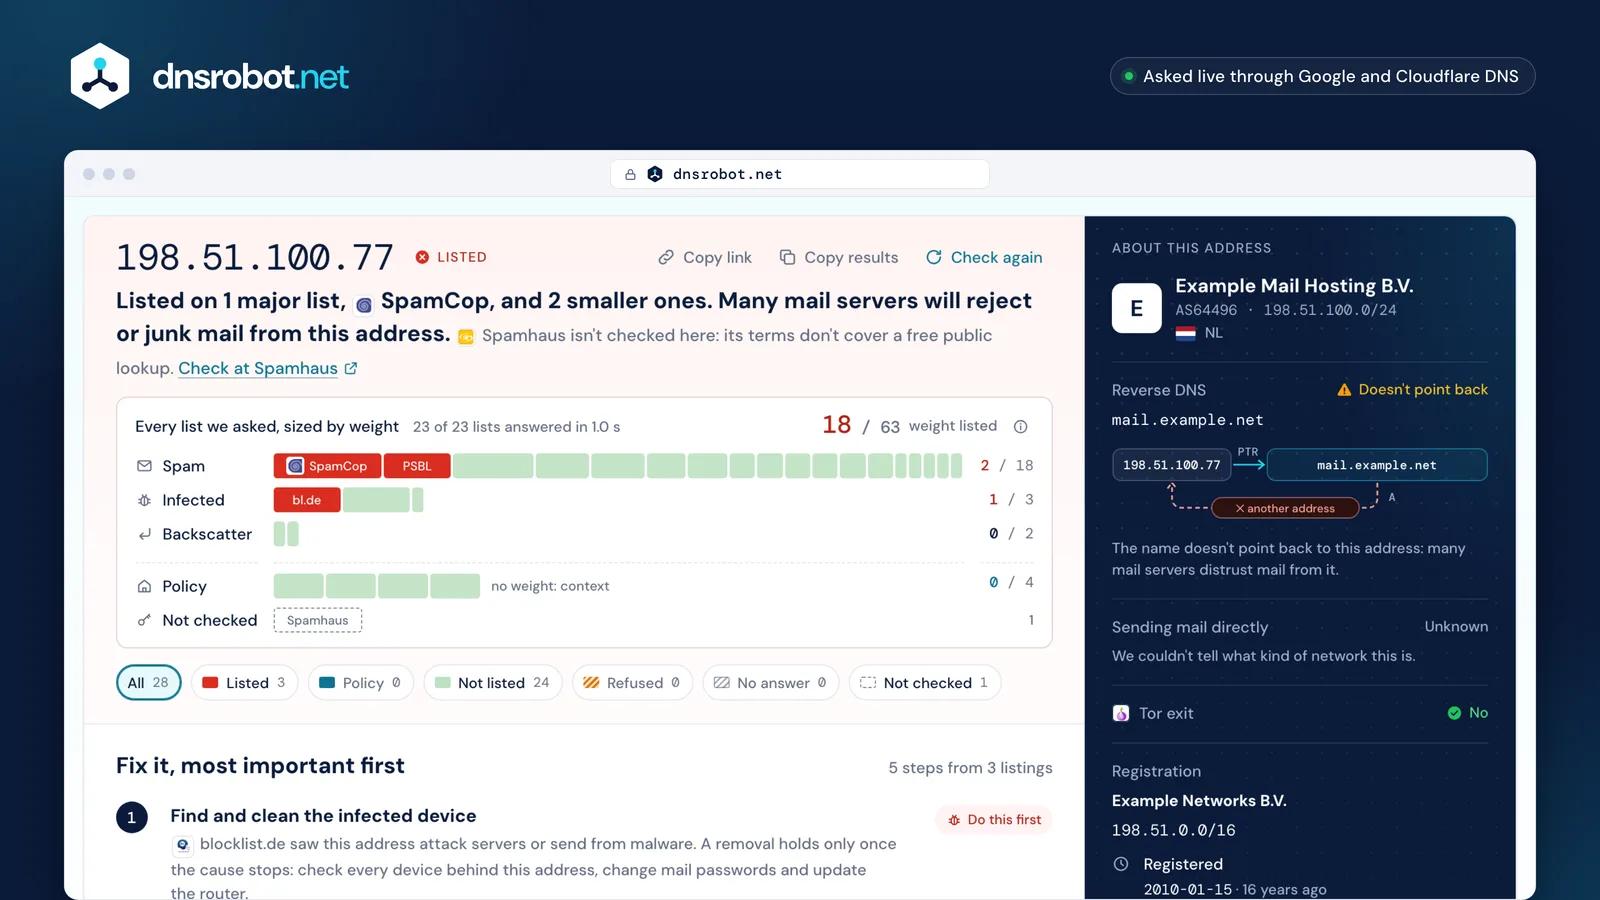
 The verdictMajor lists first, with their marks, then the smaller ones, then policy notes and the link to Spamhaus's own checker.The weight chartEvery list as a cell sized by its weight: red listed, green not listed, blue policy, hatched when it refused or didn't answer.The fix planBuilt from the listings: the cause first, then each list's removal step and how long it takes.About this addressThe network, the reverse DNS name and whether it points back, the home range, Tor, and the mail domain's SPF and DMARC.SpamCop
The list has the address. The code says why, and the list's TXT note often links to its own page about it.
 PSBL
The list answered and doesn't have the address. Counted only when the list's own test entry answered too.
A fact about the address, not an accusation: a home range, its whole network, a Tor exit. Never counted as spam.
 Spamhaus
The list refused the question. Spamhaus answers this to big public resolvers; checkers that read it as "not listed" are wrong.
Nothing came back in time, through Google or Cloudflare. Unknown, never clean: check again in a minute.
SpamhausA list we name but don't ask: its terms don't allow a free public lookup, or it has no zone for IPv6.
Spamhaus refuses public resolvers with 127.255.255.254 and Google's with no answer at all, and says plainly that this code must not be read as listed. Checkers that ask through Google or Cloudflare and show it as "not listed" give a false all-clear for the list that matters most.
The ones receiving servers actually use. SpamAssassin's default rules ask Spamhaus ZEN, SpamCop, PSBL and Mailspike; Rspamd's ask Spamhaus ZEN, Mailspike, Spam Eating Monkey and blocklist.de. Outlook.com and Yahoo both name Spamhaus in their rejections. A listing on one of these costs mail; a listing on a small personal list rarely does.
Each list here has a weight from that: who filters with it by default, what mailbox providers name, and the list's own scope. Lists of weight 6 or more are major. Policy lists weigh nothing: they describe the address, they don't accuse it.
SpamhausSpamhaus ZEN: the list most servers use. Not checked here (terms); check it at Spamhaus.Not checkedSpamCopSpam · Cisco8–PSBLSpam · Passive Spam Block List (surriel.com)5– blocklist.deAttacks · blocklist.de5–
 DroneBLAttacks · The DroneBL Team5––
 UCEPROTECT Level 1Spam · UCEPROTECT-Network4––
 InterServer RBLSpam · InterServer2––
 NordSpamSpam · The NordSpam Project2––
 SPFBLSpam · SPFBL.net2––
 ZapBLSpam · ZapBL2––
 0spamSpam · The 0spam Project2––
 anonmails.deSpam · anonmails.de1––BackscattererBounces · UCEPROTECT-Network1––UCEPROTECT Level 2Policy · UCEPROTECT-NetworkNo weight: context only––UCEPROTECT Level 3Policy · UCEPROTECT-NetworkNo weight: context only––
 Tor exits (dan.me.uk)Policy · dan.me.ukNo weight: context only––
Because something at that address did what a list watches for. The cause decides the fix: a removal request without fixing it only gets the address listed again.
Malware on a PC, phone or router behind the address sends spam or attacks other servers; a cracked mail password sends through your own server.
blocklist.deDroneBLOld, scraped or bought address lists hit addresses that never signed up for anything: the traps the lists run themselves.
PSBLUCEPROTECT Level 1ZapBLSpamCop lists addresses its users report; Mailspike and GBUdb score what they see across many mailboxes.
SpamCopA server that accepts spam and bounces it later, or auto-replies to it, sends mail to people who never wrote: backscatter.
BackscattererMail servers expect home and mobile ranges to send through the provider's server. Policy lists mark these ranges; it isn't a spam listing.
SPFBLA whole network block or provider gets listed when too many of its addresses spam, the address you checked included.
UCEPROTECT Level 2UCEPROTECT Level 3Shared exits carry other people's traffic: Tor exits are listed for what they are, abused VPNs and open proxies for what passed through.
Tor exits (dan.me.uk)DroneBLFix the cause first, then let each list do what it says. Most listings expire by themselves within days once the cause stops; the rest have a form.
Fix the cause
Clean the infected device, change the stolen password, close the open relay, stop the bounces.
Check again here
Listings that expire on their own disappear from the result as each list drops them.
Request removal where the list asks for it
Use the removal link on the list's row: its own form or lookup page.
Give it time
Each list's own time is on the timeline. A request before the fix gets the address listed again.
PSBLAbout 30 minAbout 30 minTor exits (dan.me.uk)Within an hour of the Tor relay going offlineWithin an hour of the Tor relay going offlineNordSpam1–48 h1–48 hSpamCop24 h after the last report24 h after the last reportblocklist.de48 h without attacks48 h without attacksInterServer RBL5 days5 daysUCEPROTECT Level 17 days after the last spam7 days after the last spamBackscatterer4 weeks4 weeksNever pay a third party for removal: Spamhaus says no removal ever costs money and any offer to remove a listing for a fee is a scam. UCEPROTECT sells an express removal, but its Level 1 listings expire for free 7 days after the last spam: fixing the cause and waiting costs nothing.
An email blacklist check is the same check run on the address your mail leaves from: its IP, not your e-mail address. Type the domain or an e-mail address and the checker finds its mail servers (MX) and checks them, with the domain's web address.
Not being listed is half the job. Gmail requires the sending IP to have a PTR name that points back to it (forward-confirmed reverse DNS, FCrDNS), and Yahoo asks for a meaningful, non-generic name. The result's right column checks both and, when the name has a domain, whether its SPF allows the address and whether it publishes DMARC.
Forward-confirmed
No reverse DNS
All three judge senders by their own reputation data first. Public lists still matter: Google tells senders to stay off them, and Outlook.com and Yahoo name Spamhaus when they reject mail.
Gmail's own IP reputation decides, and a very low one gets mail rejected. Google's sender guidelines still say to make sure a shared IP isn't on any internet blocklist, and require matching forward and reverse DNS.
Microsoft keeps its own blocked senders list: the bounce reads 550 5.7.606–649 and the fix is the delist portal at sender.office.com. Outlook.com's OU-001 block points to Spamhaus for removal.

Yahoo names a Spamhaus listing as a cause of permanent 5xx rejections, defers mail from addresses or ranges with poor reputation, and asks for meaningful, non-generic reverse DNS names.
Two of the three name Spamhaus, which this page can't ask: check it on Spamhaus's own page from the row in the result.
Type a domain or an e-mail address and the checker finds its mail servers (MX records), resolves them to addresses, adds the domain's web address and checks up to four addresses against every list.
Domain lists (Spamhaus DBL, SURBL, URIBL) list domain names seen in spam, not addresses. None of them allows a public lookup through Google's or Cloudflare's resolvers today: DBL is under Spamhaus's terms, SURBL needs an agreement and asks not to be used for sender addresses, URIBL refuses public resolvers. So the result says they aren't checked instead of calling the domain clean. For a link in a message, the link safety checker shows where it really goes and who blocks it.
SPF's ip4: ranges can hold thousands of addresses, too many to check one by one: check the servers that actually send.
Spamhaus DBL URIBL
Each address against every list
Ask the list's zone for the address written backwards: an answer in 127.0.0.0/8 means listed, NXDOMAIN means not. Try it with the test entry, which every list must list:
Your resolver matters: through Google or Cloudflare, Spamhaus answers 127.255.255.254 or nothing at all. Ask Spamhaus through a resolver on your own network, or on its own page.
dig +short 2.0.0.127.bl.spamcop.net AmacOS and Linux. Add TXT instead of A to read the list's note.
$ dig +short 2.0.0.127.bl.spamcop.net A
127.0.0.2
$ dig +short 2.0.0.127.bl.spamcop.net TXT
"Blocked - see https://www.spamcop.net/bl.shtml?127.0.0.2"
$ dig +short 77.100.51.198.bl.spamcop.net A
(nothing: NXDOMAIN, not listed)We'd rather name a list than show a result we can't stand behind. These are the lists other checkers still show, and why this one doesn't.
| List | Status | Why |
|---|---|---|
| Spamhaus ZEN and DBL | Terms | Free for non-commercial use only; refuses Google's and Cloudflare's resolvers. The result links to Spamhaus's own checker. |
 Barracuda BRBL | Registration | Answers only DNS servers registered with Barracuda; public resolvers can't be registered. |
 Abusix Mail Intelligence | Needs a key | Needs an API key in every question; refuses everyone else. |
 SpamRATS | Terms | Non-commercial use only, an API key, and "do not use a free DNS service". |
 Validity Sender Score | Registration | Answers registered users only; 127.255.255.255 to everyone else. |
 DNSWL | Terms | No redistribution without written approval; public resolvers get 127.0.0.255. |
 V4BL | Terms | Forbids passing any part of its lists to anyone else. |
| SURBL and URIBL | Domain list | Domain lists: SURBL needs an agreement and isn't for sender addresses; URIBL refuses public resolvers. |
 SORBS | Retired2024-06-05 | Closed by Proofpoint; every question now answers NXDOMAIN. |
| NNiX Spam | Retired2025-01-16 | Switched off; its nameservers point at documentation addresses. |
| CBL | Retired2021 | Merged into Spamhaus XBL; asking both counts one listing twice. |
| WWPBL | Retired2024 | Shut down; old mail servers still send it millions of questions a day. |
| KKISA-RBL | Retired2024-01-31 | South Korea's national list ended. |
| IINPS | Retired2020 | Shut down; its delegation says so. |
| AAHBL and emailbasura | Unreliable | Answer "listed" for every address since they closed. |
| FFabelsources | Retired | Its domain is unregistered: anyone could buy it and make it list every address. |
| JJustSpam | Unreliable | Lists Cloudflare's 1.1.1.1 resolver. |
| BBrukalai black | Unreliable | Lists Google's 8.8.8.8 resolver. |
| SSwiNOG DNSRBL | Unreliable2026-10-29 | Its test entry 127.0.0.2 stopped answering and listings now come back as 127.0.0.10, so a clean answer can't be confirmed. |
Missing something?Suggest a feature or a new tool
Is this link safe? Who blocks it, where it really redirects, how old its domain is and what the page asks for
Validate SPF records and check DNS lookup count per RFC 7208
Check any domain's DMARC policy the way receivers read it, with reports, SPF and DKIM
Find hostnames associated with any IP address via PTR records
Parse raw email headers and trace the email journey
Look up IP address geolocation, ISP, and network details instantly

